
Built around the most precious data you have — your family.
No jargon. Just honest, plain-English answers about how ITAV looks after the people you love.
Six things we'll never make you wonder about.
We don't sell your data.
ITAV makes money from the families who choose to upgrade through Apple or Google, and from small non-personalised ads on free accounts — never from data brokers. Your family's care information is never sold, shared or used for ads.
Only the people you invite can see your child.
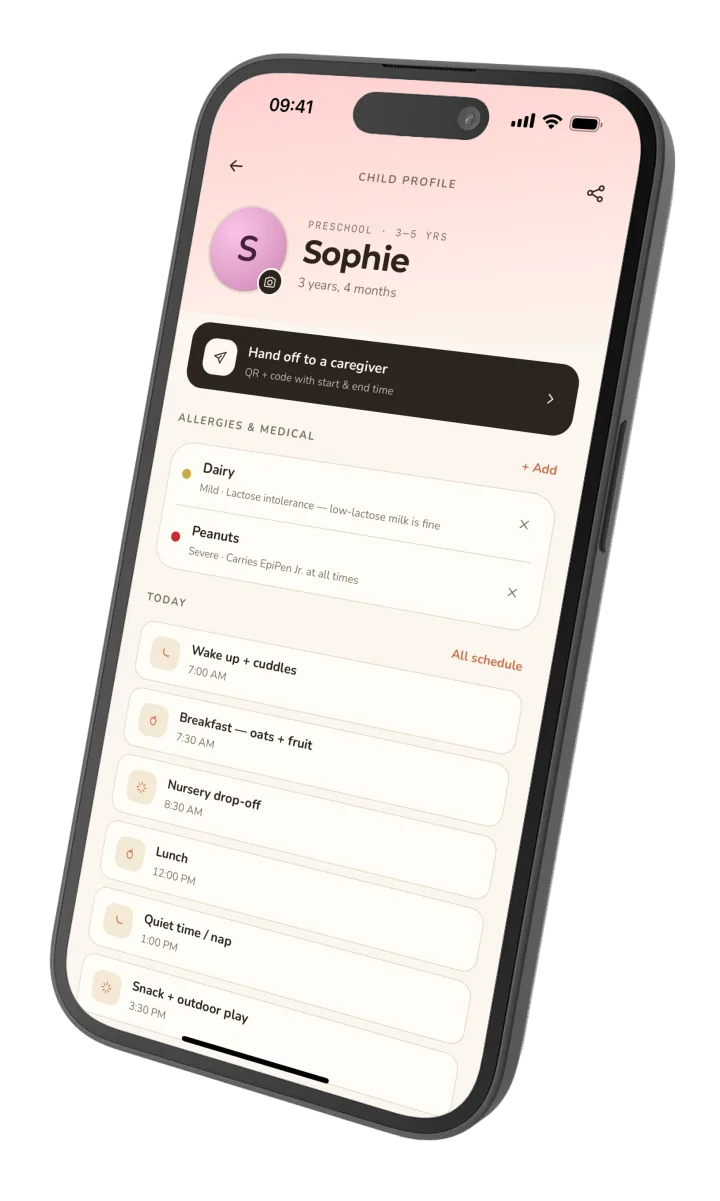
A caregiver, sitter or grandparent only reaches the child you invite them to, through a handoff you start. Their sitter snapshot shows the parts you switch on. End the session at pickup, and access ends.
Encrypted in transit and at rest.
Your data travels over HTTPS and is encrypted at rest inside our database. Sign-in is handled by Apple, Google or a trusted email flow, so we never store a password at all. Care photos and documents are served through signed, short-lived URLs, so a leaked link stops working soon after.
Location is only on when care is on.
We only see where a caregiver is during an active care session. Otherwise, nothing. The moment the session ends, the trail goes dark again.
Children never get an account.
No email, no phone number, no password, no public feed, no strangers. A child lives inside their parents’ account and is only ever seen by the village a parent has approved.
One button to take everything home.
Export every note, post and routine. Or delete it all. We don't bury those buttons three menus deep.
A clear answer to the question that matters most.
You, the parent
You see everything about your own child. You decide who else sees what — partner, sitter, nanny, grandparent, school — and you can change your mind in two taps. No setting is ever permanent.
Your invited caregiver
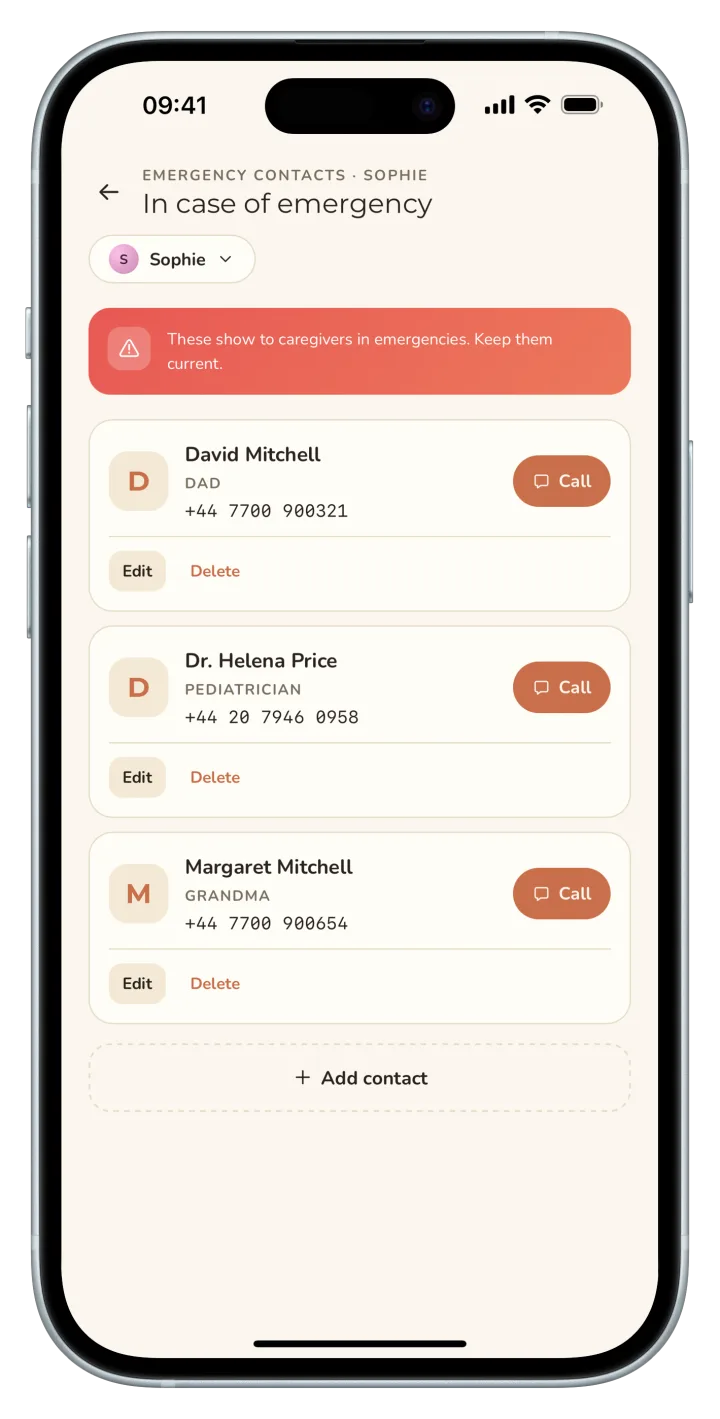
They see the child you invited them to, for the handoff you opened, and nobody else's. Their sitter snapshot shows only the parts you switched on — maybe the allergy list and today's routine, maybe also meds — plus emergency contacts. End the session and their access ends.
Other ITAV families
Other parents in the village can see the posts you write in the village feed and your public profile fields. They cannot see your child, your address, your routines or anything private. Children themselves are invisible to other users.
The ITAV team
ITAV is run by a deliberately small team — support is answered by the person who built the app, not a call centre. Day to day, nobody at ITAV reads your private notes, photos, posts or location; account-level records are accessed only when you ask for support, or when the law requires it.
What we do behind the scenes — without the buzzwords.
Encrypted on the way and at rest
Every connection between your phone and ITAV is encrypted. Your data is encrypted while it sits on our servers, too. If anyone got hold of the storage, they would see scrambled noise.
Sign-in by Apple, Google or email
We use a trusted sign-in service so we never see or store your password. Suspicious sign-in attempts are blocked automatically.
Every request is checked
Every time the app asks for information about your child, we check that the person asking is allowed to see it — before any data is loaded. There is no way to "guess" your way to someone else's child.
Abuse and spam are blocked at the door
We limit how often the app can be hit from a single account or IP address. People trying to brute-force a code, scrape data or spam the village hit a wall almost immediately.
Location is treated as sensitive
Location pings are recorded only during an active care session. They are never used for marketing, and they never appear in our debug logs.
Deletions stick
When you delete your account it is removed from our live database straight away, not just hidden. Backups roll off on a fixed window — see the Privacy Policy. After that it is genuinely gone.
The strictest corner of ITAV.
No accounts for children
Children never sign in, so we never ask a child for an email address, phone number, password or photo of themselves. Their profile lives with their parents.
Shared only by a parent
A child’s details reach another adult only through something a parent sets up — a caregiver handoff, a facility QR or a snapshot link — and you can end or revoke each one.
A record of your consent
Every consent you give — terms, privacy, children’s data, location — is stored with the policy version and the moment you gave it, and you can withdraw it at any time.
A safe word at pickup
Add a safe word to a pickup so the adult collecting your child can prove they are the right one.
POPIA & COPPA, by design
ITAV is designed for South Africa's POPIA (which treats anyone under 18 as a child) and the U.S. Children's Online Privacy Protection Act, plus the EU/UK rules protecting children online.
No public child community
Children cannot post, cannot be searched, cannot be messaged by anyone. Their world inside ITAV is small on purpose.
What we do, and what we promise.
If you spot a security issue
Researchers, parents and curious humans are all welcome to tell us about anything that looks wrong. Email hello@itavapp.com and we'll reply within a working day. We don't take legal action against people who report problems in good faith.
If a child is at risk
If you are worried about a child because of something you've seen on ITAV, email hello@itavapp.com. Safeguarding reports jump every other queue: we can freeze accounts, preserve evidence and cooperate with local authorities. ITAV is not itself an emergency service — if there is immediate danger, please call your local emergency number first.
Where your data lives
One primary database — Cloudflare D1, held in the EU jurisdiction and encrypted at rest — with photos and files in Cloudflare R2, also in the EU. The ITAV API runs on Cloudflare Workers. The full provider list, with regions, is on the compliance page.
If we have a data incident
If something happens that affects your data, we will tell you about it honestly and quickly — and we will tell the relevant regulator (the Information Regulator in South Africa, your data protection authority in the EU/UK) within the timeframes the law requires. We will explain what happened, what we've done about it, and what you can do.